Cybersecurity Newsfeed - 30/09/26
Daily cybersecurity news covering vulnerabilities, adversaries, trends, breaches, and other notable security developments.
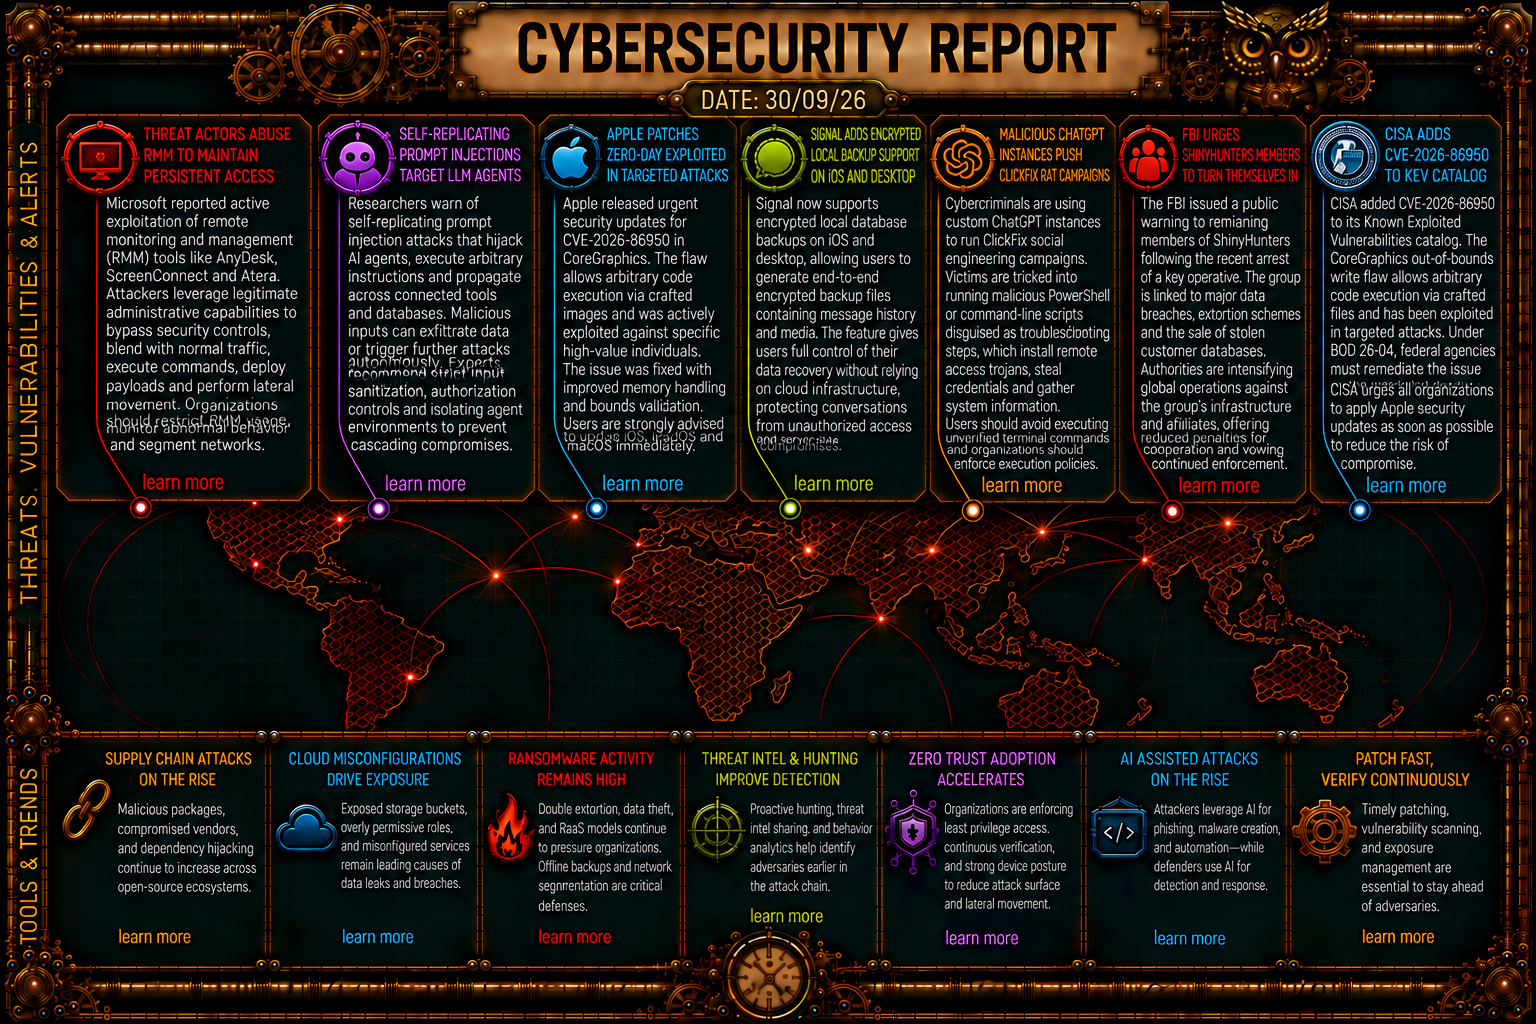
Cybersecurity Newsfeed
📅 30/09/26
🛡️ Vulnerabilities
Apple CoreGraphics Zero-Day Exploited in Targeted Attacks: Apple released urgent security updates to address an actively exploited out-of-bounds write flaw in CoreGraphics. Processing maliciously crafted images allows arbitrary code execution on vulnerable iOS, iPadOS, and macOS devices. More info More info More info More info CISA Adds Apple Flaw (CVE-2026-86950) to KEV Catalog: CISA added CVE-2026-86950, an out-of-bounds write flaw affecting iOS, iPadOS, macOS, watchOS, and tvOS, to its Known Exploited Vulnerabilities Catalog. Federal agencies must patch promptly to mitigate remote code execution risks. More info
Citrix NetScaler Zero-Day Exploited for Web Shell Deployment: Threat actors are exploiting an unauthenticated remote code execution zero-day vulnerability in Citrix NetScaler ADC and Gateway appliances to deploy persistent web shells, harvest credentials, and perform lateral movement. More info
New Spectre v2 Variant Leaks Linux Root Password Hashes: Researchers disclosed a new Spectre v2 speculative execution attack variant capable of extracting kernel memory contents—including root password hashes—within minutes via microarchitectural timing side channels. More info
🎯 Adversaries
Phishing Abuses RMM Tools for Persistent Access: Microsoft Security detailed how threat actors exploit legitimate remote monitoring and management tools like AnyDesk, ScreenConnect, and Atera to maintain persistent network access and bypass security controls. More info
Automated AI Agent Breaches Cybersecurity Nonprofit DIVD: An autonomous AI agent exploited exposed configuration flaws to breach internal networks of the Dutch Institute for Vulnerability Disclosure (DIVD), gaining administrative privileges without human intervention. More info
101 Malicious npm Packages Target Developer Credentials: Security researchers uncovered 101 typosquatted npm packages that execute malicious installation scripts to steal API keys, SSH credentials, and environment variables from developer workstations. More info
NeedyMantis Malware Expands to Cloud & Hybrid Environments: The NeedyMantis campaign updated its post-exploitation framework with new modules targeting Active Directory and enterprise cloud infrastructure for credential harvesting and lateral movement. More info
- JadePuffer Hijacks Azure Identities for Resource Abuse: Threat actors compromised Azure enterprise credentials to spin up high-performance virtual machines for unauthorized cryptocurrency mining, leading to severe cloud utility costs for victim organizations. More info
📈 Trends
Self-Replicating Prompt Injection Attacks Threaten AI Workflows: Researchers warned of self-propagating prompt injection vulnerabilities in LLM agents, which allow hidden malicious instructions in text or web content to hijack AI workflows and spread autonomously across tools. More info
Signal Adds Encrypted Local Backup Support to iOS and Desktop: Signal introduced end-to-end encrypted local database backups for iOS and desktop apps, providing user-controlled message history and media recovery independent of cloud infrastructure. More info
Windows 11 2026 Update Introduces Advanced AI Security: Microsoft released the Windows 11 2026 Update, featuring smart application control, hardened credential isolation, and refined memory protection defaults to defend against zero-day exploits. More info
RemoteThreat Launches Offensive Operations Platform: Security startup RemoteThreat secured $7 million in funding to build an automated platform that continuously simulates adversary tactics and identifies network misconfigurations. More info
💥 Breaches & Leaks
- French Tax Authorities Suffer Data Breach via Stolen Credentials: Cybercriminals used compromised administrative credentials to gain unauthorized access to French tax authority systems, exfiltrating personal identities, tax IDs, and income records. More info
📚 Others
FBI Warns ShinyHunters Members Following Operative Arrest: The FBI urged remaining members of the ShinyHunters cybercrime group to surrender following a major operative arrest, warning of intensified global law enforcement operations. More info
Former U.S. Air Force Members Sentenced for BEC Attacks: Two former Air Force personnel were sentenced to prison for executing business email compromise (BEC) schemes targeting government contractors and laundering millions in illicit funds. More info
Vietnamese National Charged in $16M Pig Butchering Crypto Scam: Federal prosecutors charged a Vietnamese national for operating a global $16 million romance-based investment scam that laundered funds through cryptocurrency networks. More info