Cybersecurity Newsfeed - 04/11/26
Daily cybersecurity news covering vulnerabilities, adversaries, trends, breaches, and other notable security developments.
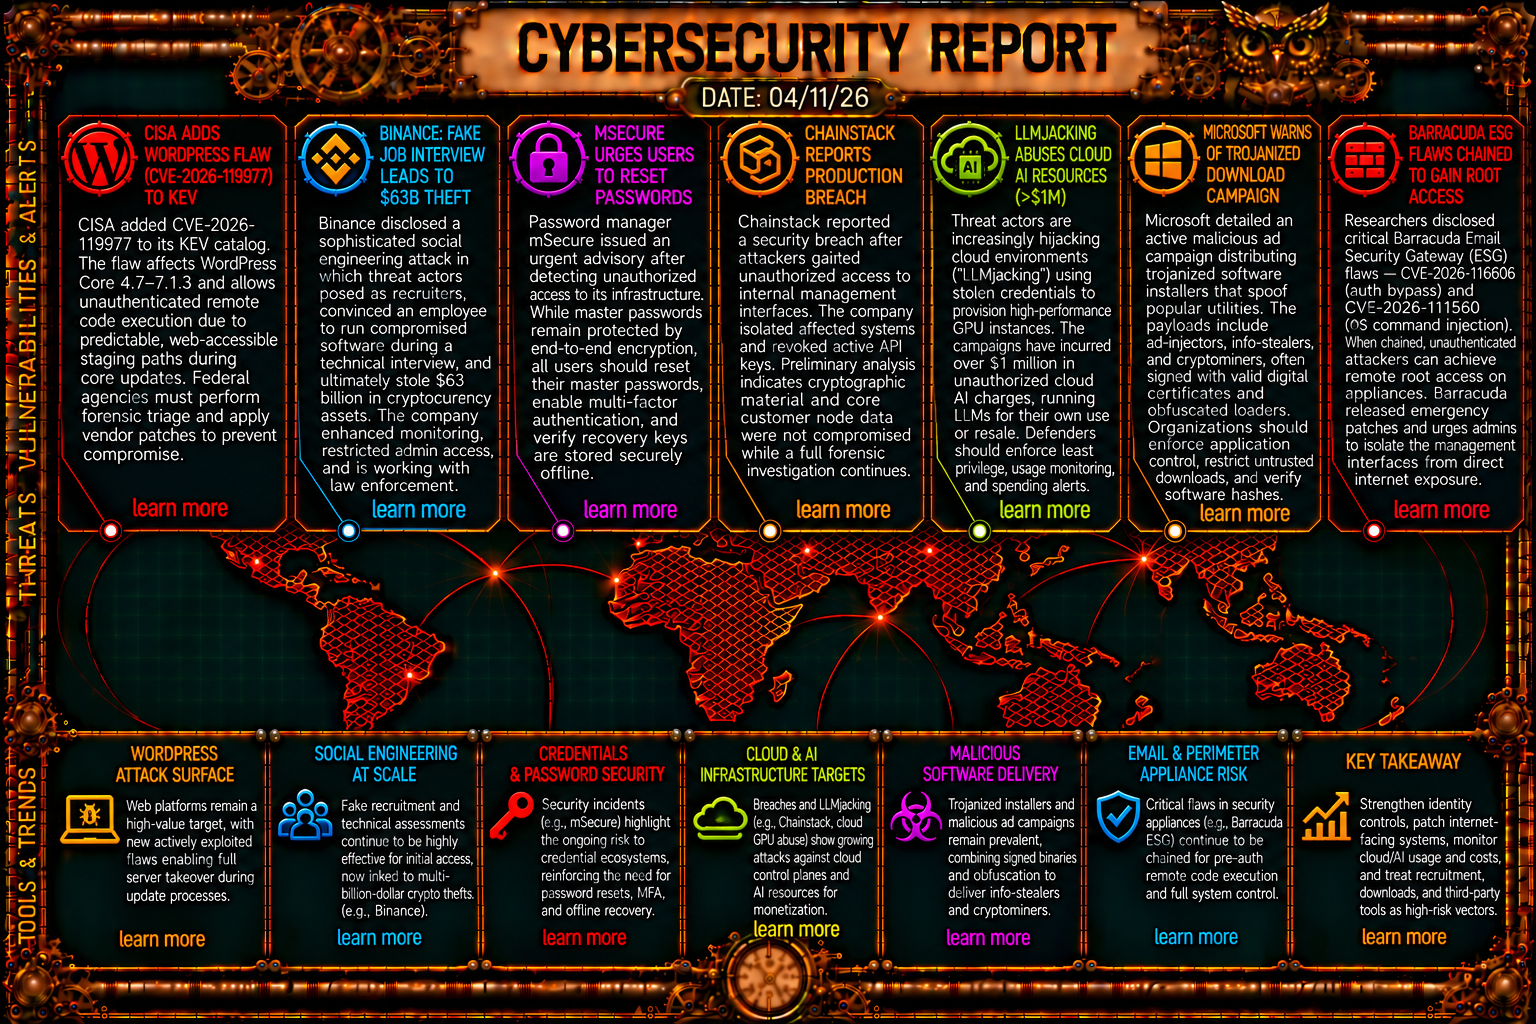
Cybersecurity Newsfeed
📅 04/11/26
🛡️ Vulnerabilities
WordPress Core Race Condition (CVE-2026-119977): CISA added CVE-2026-119977 to its Known Exploited Vulnerabilities Catalog affecting WordPress Core versions 4.7 through 7.1.3. The flaw stems from predictable, web-accessible staging paths during updates, allowing unauthenticated remote attackers to execute arbitrary code. More info
Node-RED ICS Authentication Flaw (CVE-2026-58115): Threat actors are actively exploiting a CVSS 10.0 vulnerability in Node-RED environments integrated into industrial control system (ICS) devices to execute arbitrary commands and deploy Linux botnet malware. More info
- Red Hat Linux Kernel TCP Stack RCE (CVE-2026-98432): Red Hat issued patches for a CVSS 9.8 critical Linux kernel TCP stack vulnerability that allows unauthenticated remote attackers to trigger memory corruption and achieve root remote code execution via crafted IPv4 requests. More info
🎯 Adversaries
Trojanized Software Installers via Malicious Ads: Microsoft published research detailing an active ad campaign distributing trojanized software downloads containing ad-injectors, info-stealers, and crypto miners signed with valid digital certificates. More info
3am Ransomware Hits UK Educational Systems: The 3am ransomware group used automated AI-driven scanning tools to rapidly identify perimeter vulnerabilities and execute lateral movement across UK school system networks. More info
CPGuard Server Security Update Hijacking: Attackers compromised CPGuard’s software update delivery infrastructure to push tampered binaries containing backdoors with administrative execution privileges. More info
Pre-Installed Backdoor on 1.3M Android TV Boxes: Security analysts uncovered a persistent firmware backdoor active on over 1.3 million Android-based TV set-top boxes, enlisting them into a global botnet for DDoS operations and proxy routing. More info
- SSH Backdoors Hidden in Cursor & Claude Code Extensions: Malicious extensions targeting developer environments silently deploy scripts designed to extract local SSH keys, user credentials, and active terminal session tokens. More info
📈 Trends
Gartner Predicts Shift to SOC Engineers by 2028: Gartner forecasts that SOC engineering roles will outnumber security analyst roles by 50 percent by 2028, driven by AI automation and detection-as-code paradigms. More info
Unit 42 October 2026 Threat Intelligence Digest: Palo Alto Networks Unit 42 published its monthly threat intelligence digest highlighting increased edge network device exploitation, ransomware double-extortion tactics, and cloud identity risks. More info
💥 Breaches & Leaks
mSecure Infrastructure Incident Prompts Password Resets: Password management provider mSecure instructed all users to reset their master passwords following unauthorized infrastructure access, mitigating potential brute-force risks against encrypted vaults. More info
Chainstack Production Systems Breach: Blockchain infrastructure provider Chainstack isolated infrastructure and revoked API keys after attackers gained unauthorized access to internal management interfaces. More info
📚 Others
Security & Privacy Guide for Crypto Debit Cards: A consumer guide highlights critical operational and security considerations prior to adopting cryptocurrency debit cards, including custodial risks and fraud protection mechanisms. More info
Cogent Security Named to Fortune Cyber 60: Cogent Security secured a spot on the Fortune Cyber 60 list for the second consecutive year for its factory-like operational model applied to cyber defense operations. More info