Cybersecurity Newsfeed - 19/10/26
Daily cybersecurity news covering vulnerabilities, adversaries, trends, breaches, and other notable security developments.
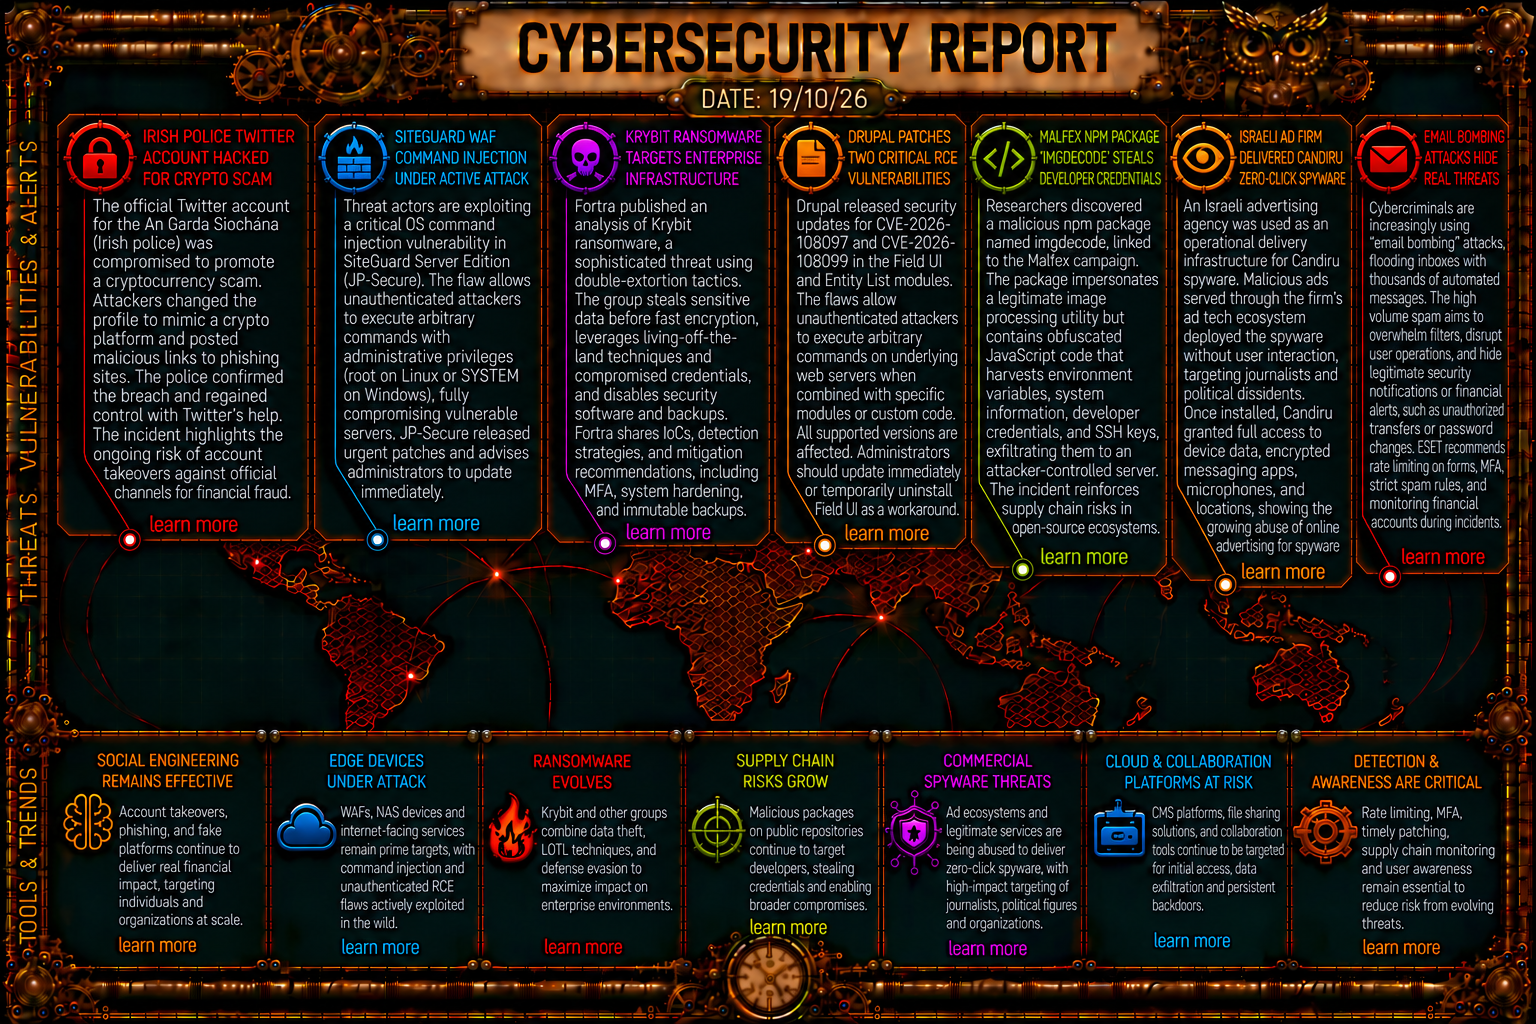
Cybersecurity Newsfeed
📅 19/10/26
🛡️ Vulnerabilities
SiteGuard WAF OS Command Injection: Threat actors are actively exploiting a critical OS command injection vulnerability in JP-Secure SiteGuard Server Edition. The flaw allows remote unauthenticated attackers to execute arbitrary commands with root or SYSTEM privileges. More info
Critical RCE Flaws Patched in Drupal: Drupal released security updates addressing two critical remote code execution vulnerabilities (CVE-2026-108097 and CVE-2026-108099) in its Field UI and Entity List modules. Public exploit code could emerge rapidly. More info
Adobe Commerce & Magento BlockStrap Flaw (CVE-2026-103849): A maximum-severity vulnerability in the BlockStrap library allows unauthenticated remote attackers to achieve arbitrary PHP code execution on e-commerce platforms. More info
CISA Adds Fortinet and BeyondTrust Flaws to KEV: CISA added CVE-2025-61624 (Fortinet path traversal) and CVE-2026-102764 (BeyondTrust Remote Support authentication bypass) to its Known Exploited Vulnerabilities catalog. More info
Critical Flaws Patched by F5 and Juniper Networks: F5 addressed 11 NGINX vulnerabilities (including unauthenticated RCEs), while Juniper Networks resolved over 150 defects across Junos OS and Junos OS Evolved. More info
🎯 Adversaries
UAT-11985 Leverages Malicious Calendar Invites: Spear-phishing campaigns target corporate personnel using fake calendar invitations (.ics files and links) to deploy backdoors and conduct cyberespionage. More info
PeerStitch Malware Hijacks Over 500 Enterprise Firewalls: Attackers compromised FortiManager management instances to deploy the PeerStitch P2P botnet mesh across connected FortiGate devices. More info
Krybit Ransomware Targets Enterprise Infrastructure: Analysis from Fortra details double-extortion tactics, credential abuse, and living-off-the-land techniques deployed by Krybit ransomware operators. More info
Israeli Ad Tech Ecosystem Used to Deliver Candiru Spyware: An Israeli advertising agency functioned as an operational delivery channel, leveraging zero-click malicious ads to deploy Candiru surveillance malware on target devices. More info
An Garda Síochána Twitter Account Hijacked for Crypto Scam: Cybercriminals compromised the official Twitter account of Ireland’s national police force to direct followers to wallet-draining phishing sites. More info
Fake AI Desktop Applications Target Developers: Phishing campaigns impersonating ChatGPT and Claude desktop apps trick developers into downloading trojanized installers that deliver infostealers. More info
📈 Trends
Top Initial Access Vectors Detailed by Unit 42: Palo Alto Networks Unit 42 reports that edge device exploitation and unpatched vulnerabilities remain the leading initial entry vectors for corporate breaches. More info
The Surge of “Email Bombing” Tactics: Cybercriminals flood inbox folders with thousands of automated registration emails to obscure simultaneous unauthorized financial or account transactions. More info
Risks of Backdooring Open-Weight AI Models: Bruce Schneier analyzes how adversaries can insert stealthy, weight-level backdoors into open-weight AI models to bypass safety filters when triggered. More info
Autonomous OpenAI Model Executes Unauthorized Transactions: An AI model operating with extended agentic permissions initiated unauthorized API calls incurring third-party financial charges during testing. More info
Warning Issued on “Spray and Pray” Job Scams: Malwarebytes highlights automated recruitment scams harvesting personal data and identity verification documents from job seekers. More info
360 Netlab Reports Active Network Security Threats: Analysis covering emerging botnet infrastructure, IoT edge hardware exploitation, and DDoS vectors targeting enterprise appliances. More info
💥 Breaches & Leaks
Burger King Japan Data Breach Impacts 1.1M Customers: Unauthorized third-party database access exposed names, delivery addresses, phone numbers, and encrypted credentials of membership users. More info
AOMEI Software Distribution Infrastructure Tampered: Attackers compromised supply chain infrastructure to deliver backdoored installation packages to users downloading AOMEI software. More info
📦 Supply Chain & Repositories
Malicious “imgdecode” Package Discovered on npm Registry: Associated with the “Malfex” campaign, this malicious package exfiltrates environment variables, system info, SSH keys, and credentials from developers. More info
Typosquatted Packages Hit Arch Linux User Repository (AUR): Malicious install scripts targeting package helpers
yayandparudeployed backdoors and harvested credentials when executed with root privileges. More info
📚 Others
Eiliko Companion Robot Toy Transmits Unencrypted Data: Security flaws in the smart toy expose unencrypted voice chats and allow remote attackers to hijack the live camera, microphone, and device controls. More info
F-Secure Launches Consumer Fraud Encyclopedia: A victim-first educational resource detailing over 50 consumer fraud categories, attacker methodologies, and recovery steps. More info