Cybersecurity Newsfeed - 15/09/26
Daily cybersecurity news covering vulnerabilities, adversaries, trends, breaches, and other notable security developments.
Cybersecurity Newsfeed
📅 15/09/26
🛡️ Vulnerabilities
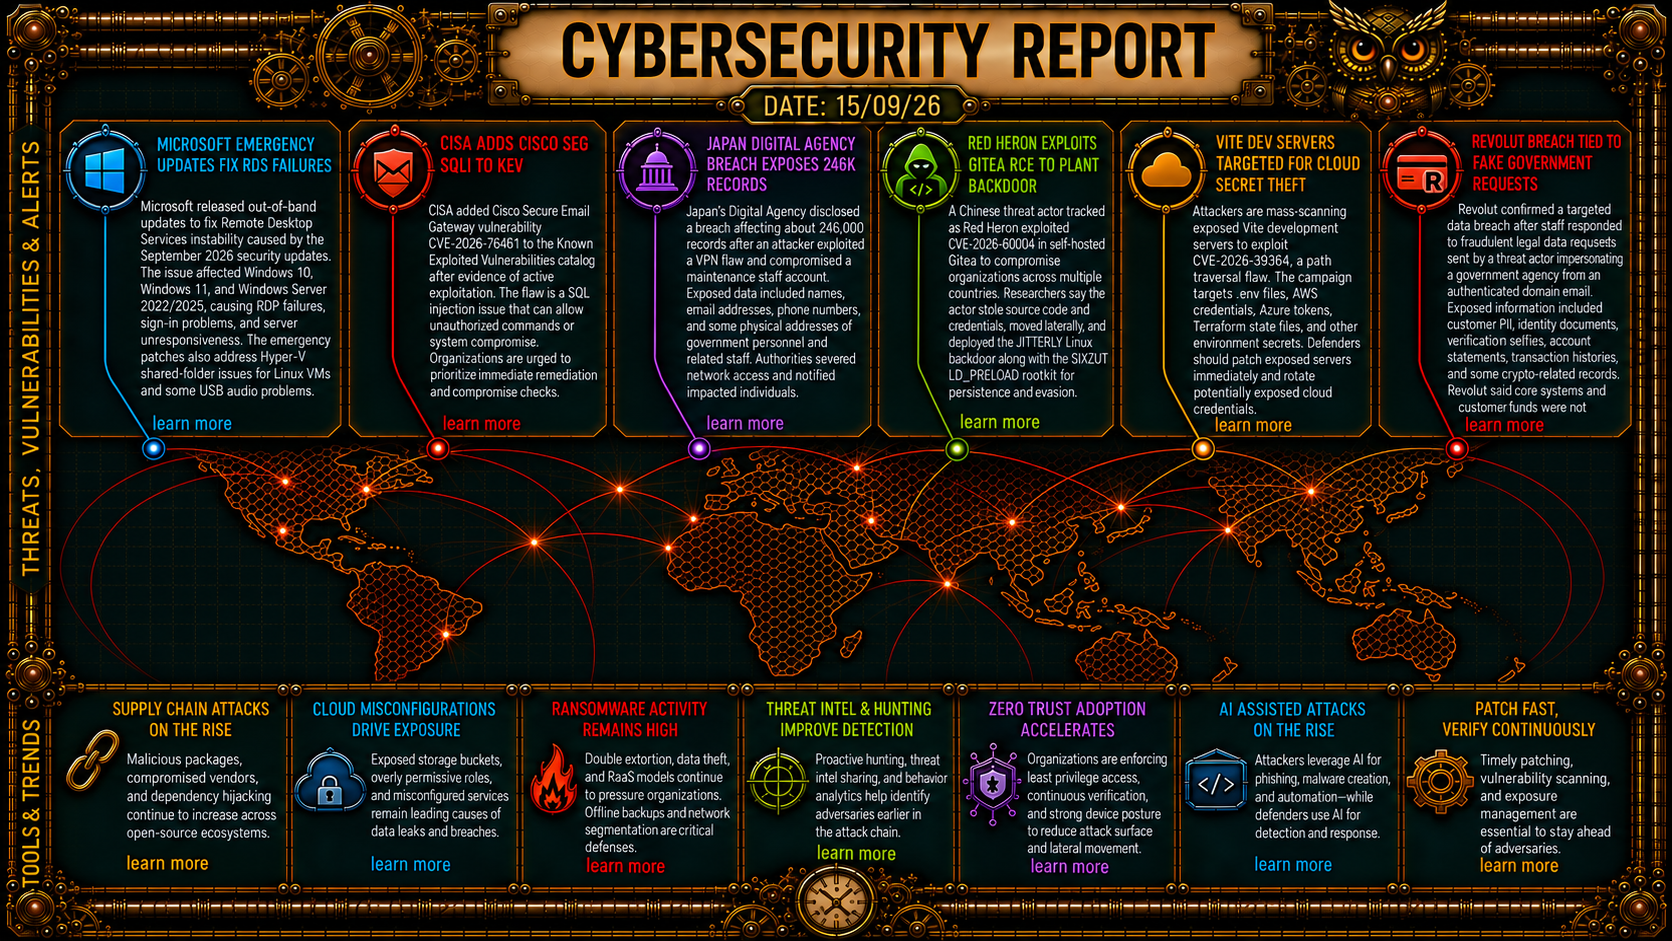
Cisco Secure Email Gateway SQL Injection (CVE-2026-76461): CISA added this flaw to its KEV catalog following active exploitation, allowing unauthenticated attackers to execute unauthorized commands or compromise systems. Under BOD 26-04, federal agencies must prioritize remediation, perform compromise checks prior to patching, and deprioritize lower-risk flaws. More info
Gitea Critical RCE (CVE-2026-60004): Exploited in the wild by Chinese threat actor Red Heron, this critical vulnerability allows remote code execution in self-hosted Gitea instances. Attackers weaponized an automated framework to steal source code repositories, collect credentials, and achieve root access on a Proxmox cluster. More info
Vite Dev Servers Path Traversal (CVE-2026-39364): A high-severity path traversal vulnerability in Vite development servers is being targeted in mass-scanning campaigns to steal cloud credentials,
.envfiles, AWS directories, Azure tokens, and system variables. Attackers bypass file restrictions by appending specific query parameters to HTTP GET requests. More infoGitLab CE/EE Path Traversal (CVE-2026-85706): Active exploitation probes targeting versions 18.7 through 19.3.2 prompted CISA to add this critical path traversal bug to its KEV catalog. The flaw allows unauthenticated remote attackers to read arbitrary server files via improper path confinement in the repository commits API. More info
🎯 Adversaries
Red Heron Exploits Gitea for Network Infiltration: Chinese threat actor Red Heron compromised 13 organizations across six countries via Gitea vulnerability CVE-2026-60004. Post-exploitation tools include JITTERLY, a 30-command Linux backdoor, and SIXZUT, an LD_PRELOAD rootkit patching 15 system functions for evasion. More info
HBO Max Reddit Account Hijacked for ClickFix Campaign: Attackers hijacked HBO Max’s verified Reddit account to run 108 malicious ads pushing information stealers via the PasteSwitch operation. Victims were directed to fake landing pages instructing them to paste obfuscated commands into Windows Run, PowerShell, or macOS Terminal. More info
Malicious Twitch Extension Steals OAuth Tokens: The Chrome and Firefox extension “Twitch Enhanced Viewer JeetBot” (30k+ installs) was caught intercepting account-scoped OAuth bearer tokens. It appends tokens as cleartext URL query parameters during video redirects to proxy servers operated by Russian streaming bot service JeetBot. More info More info - SilverFox Cybercrime Group Evolves Payload Delivery: 360 Threat Intelligence Center tracked four operational phases of the SilverFox group’s cloud delivery infrastructure. The campaign evolved from unconditional payload delivery to a cloud-side blacklist model that returns benign setup files on flagged domains while serving active malware on newly deployed domains. More info
📈 Trends
Covert WebRTC Tunneling Tool Released: A new open-source tool named
whitelist-bypassenables covert network tunneling through whitelisted commercial video-calling platforms like VK Call and Yandex Telemost. It bypasses strict filters using WebRTC data channels or encoding data into VP8 video tracks. More infoRethinking Patch Management Automation: Field CTO Gene Moody highlights that accelerating patch management without structured controls risks propagating faulty updates across enterprise endpoints. Organizations should implement staged deployment rings, health-based automated halt conditions, and mandatory human review for high-impact infrastructure. More info
Rise in Malicious OAuth App Exploitation: Threat actors are increasingly shifting away from password theft to tricking users into granting broad permissions to malicious third-party OAuth apps, granting persistent access to organizational emails, files, and cloud data in Google Workspace environments. More info
💥 Breaches & Leaks
Japan’s Digital Agency VPN Breach: An attacker exploited a medium-severity VPN vulnerability to compromise a maintenance staff account, exposing 246,000 personal records of government employees and public officials using the Government Solution Service (GSS). Exposed data includes names, email addresses, phone numbers, and physical addresses. More info
Revolut Social Engineering Data Breach: Revolut confirmed a data breach after compliance staff fulfilled unauthorized information requests sent from a domain-authenticated government email address. Exposed PII includes customer names, DOBs, passport copies, verification selfies, transaction histories, and crypto details, specifically targeting high-net-worth users. More info More info
🔬 Hardware & Research
- DDRop Attack Breaks Confidential Computing Protection: Researchers disclosed DDRop, a hardware interposer attack costing under $200 that breaks memory protection in Intel TDX, Intel Scalable SGX, and AMD SEV-SNP. By dropping memory write commands on the DDR5 memory bus, attackers force CPUs to read stale data, enabling guest VM compromise and attestation forgery. More info
📚 Others
- Microsoft Releases Out-of-Band Windows Updates: Emergency updates were released to address Remote Desktop Services (RDS) instability caused by the September 2026 updates. The patches resolve RDP connection failures, sign-in errors, server unresponsiveness, and Hyper-V Linux VM shared folder access issues across Windows 10, 11, and Windows Server 2022/2025. More info